cTLS
Session Keys
Ephemeral RAM-only keys for forward secrecy
Session Key Management
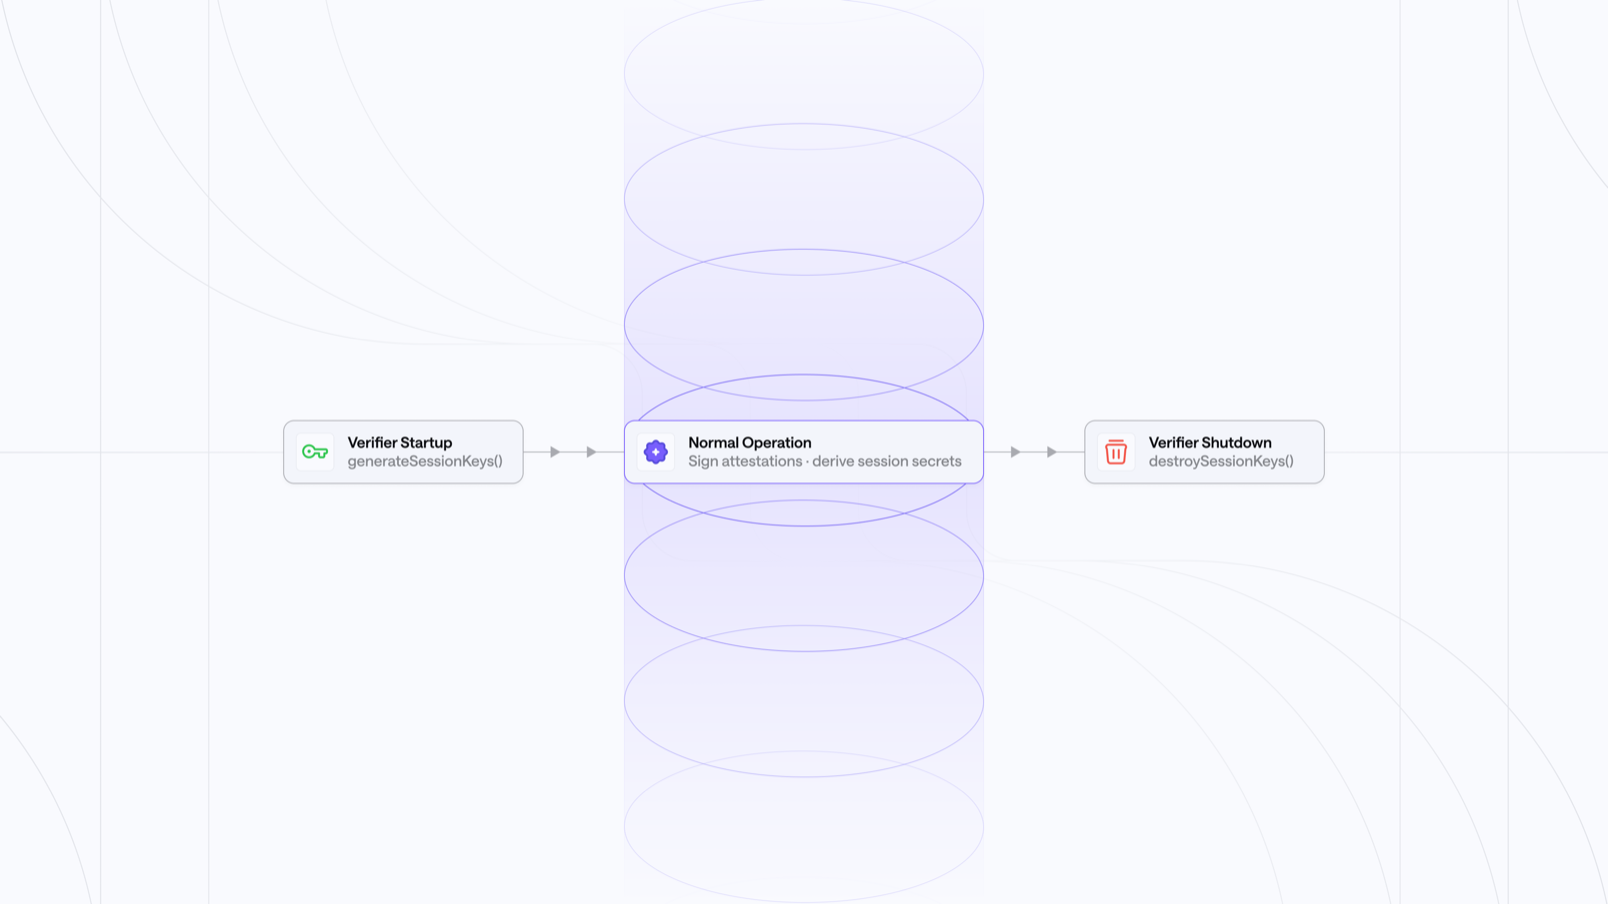
cTLS uses ephemeral session keys for forward secrecy. Keys exist only in Verifier RAM and are destroyed on shutdown.
Session Keys Structure
interface SessionKeys {
  /** Ed25519 public key shared with clients for signing verification */
  publicKey: string;
  /** Ed25519 private key - RAM-only, never persisted */
  privateKey: string;
  /** X25519 public key for ECDH key agreement (encryption) */
  x25519PublicKey: string;
  /** X25519 private key - RAM-only, never persisted */
  x25519PrivateKey: string;
  /** When the keys were created */
  createdAt: number;
}
Forward Secrecy Guarantees
Session keys are never persisted to disk. They exist only in RAM during the Verifier’s lifetime.
This means:
- Each Verifier restart generates fresh keys
- Past communications cannot be decrypted even if storage is compromised
- Agents must re-register after Verifier restarts